Author: Rebecca Rettig, COO & Chief Legal Officer, Jito Labs
Translation: Chopper, Foresight News
Many financial institutions are leveraging one of the most innovative advances in blockchain technology: permissionless networks.
Franklin Templeton has been keeping the official share register for its on-chain U.S. Government Money Fund on a permissionless blockchain since 2021 and integrated with the Solana network in February 2025. BlackRock has been issuing shares of its tokenized money market fund on Ethereum since March 2024. In January 2025, Apollo extended tokenized access to its diversified credit fund across six permissionless networks. Announcements about traditional financial institutions deploying products on permissionless networks appear almost weekly.
However, some traditional financial institutions still consider permissionless networks unworkable. Instead, many banks, broker-dealers, and asset managers are gravitating toward permissioned networks — systems where a gatekeeper or consortium decides who can validate transactions, who can use or participate in the network, and for what purposes. These institutions currently choose permissioned networks because they mistakenly believe they must. The underlying premise for this choice is that a known and vetted set of participants is a prerequisite for compliance with financial integrity laws, such as the Bank Secrecy Act (BSA) and its Anti-Money Laundering (AML) and Countering the Financing of Terrorism (CFT) requirements, as well as U.S. sanctions laws.
In short, institutional compliance departments see permissionless networks as irreconcilable with the BSA and sanctions laws.
Our new paper, "The Compatibility of Permissionless Networks with Financial Integrity: A Practical Guide for Financial Institutions" (https://papers.ssrn.com/sol3/papers.cfm?abstract_id=7343938), clarifies that financial institutions can build and transact on permissionless blockchain networks. Concerns about financial integrity laws should not hinder such use, and these issues can be resolved today under existing law. Institutions can fulfill their obligations through an appropriate, risk-based compliance framework that places controls at the level of the institution's operations.
Financial institutions do not need any prerequisite — regulatory or otherwise — to own, inspect, or control the underlying infrastructure on which their financial transactions and related information travel. Indeed, regulators have explicitly recognized that financial institutions can adapt their financial integrity compliance programs to technological innovations like permissionlessness.
Requirements of Financial Integrity Laws
The BSA and sanctions laws require financial institutions to have reasonable control over risks and to implement controls to mitigate such risks. They do not require the elimination of all risk, an impossible threshold.
Under the BSA, a financial institution's AML/CFT program must focus on detecting, documenting, and deterring illicit financial activity. These programs are not designed to comprehensively prevent money laundering or terrorist financing; they cannot. Federal banking regulators and FinCEN have made clear that financial integrity hinges on an AML program that is "reasonably designed," which includes "effective processes to identify, measure, monitor, and control risk."
FinCEN put this more bluntly in its August 2020 enforcement statement, describing its approach to BSA enforcement as not a "gotcha" game. The Treasury's report on de-risking directly addresses this latent concern, noting that while banks perceive any failure in bank controls as exposing them to massive fines, regulators point out such fines are rare and typically follow a complete collapse of an AML/CFT program, not the limited shortcomings that a risk-based approach sometimes yields.
The sanctions regime follows a similar logic. OFAC's Framework for OFAC Compliance Commitments identifies five essential components of an effective, risk-based sanctions compliance program: management commitment, risk assessment, internal controls, testing and auditing, and training.
OFAC tailors its expectations for implementation based on an institution's size, products, customers, and geographic reach.
OFAC's Economic Sanctions Enforcement Guidelines weigh factors like willfulness, awareness of conduct, harm to sanctions objectives, and adequacy of a compliance program when deciding how to treat an apparent violation.
The separate enforcement regimes and histories of the agencies support an approach of "risk balance, not zero tolerance." FinCEN and OFAC focus enforcement on reasonably knowable systemic deficiencies, not isolated misses. This position bears directly on institutional concerns about inadvertent violations with permissionless networks.
Both AML/CFT and sanctions mechanisms require controls proportionate to identified risks, and financial institutions can achieve this on permissionless networks. Any minor or inadvertent breach of these mechanisms should not pose a risk to a financial institution.
Inadvertent, Indirect Interactions Do Not Constitute Sanctions Violations
Financial institutions should understand the use of a permissionless network as analogous to the use of infrastructure, much like they treat the public internet and telephone networks. Both are shared systems, whose other users and operators they neither know nor vet. They should accordingly tailor their compliance strategies.
Instead, a major reason financial institutions are reluctant to engage on permissionless networks is the fear of interacting inadvertently or unknowingly with sanctioned or illicit actors — for example, paying network fees to a validator operated by a sanctioned actor, transacting unknowingly with a sanctioned actor, or receiving or trading crypto assets that may have touched illicit actors at some point in their history.
However, inadvertent, unknowing interactions with validators or other network participants from sanctioned jurisdictions are not the type of activity sanctions laws aim to address. This concern is broader than geography, as a validator can be a Specially Designated National (SDN) anywhere: the institution has not chosen, contracted with, exported to, funded, or otherwise transacted with that party, and the fees reach that actor through the same rules that apply to all network users.
Regulators have confirmed this. For instance, in November 2025, the OCC responded to this concern by issuing Interpretive Letter 1186, confirming that banks can pay network fees on blockchain networks and can hold as principal the crypto assets needed to pay those fees. The letter reasoned from Interpretive Letter 1174 from January 2021, in which the OCC concluded that banks could validate, store, and record payment transactions by acting as nodes. Accepting fees paid to a node was a corollary of that conclusion. The letter used the Ethereum blockchain as an example, a permissionless network whose protocol selects validators pseudorandomly. Neither letter distinguished between permissioned and permissionless networks.
When an institution submits a transaction via a permissionless network, the protocol assigns the right to propose the block containing that transaction to a single validator, typically pseudorandomly and proportional to stake. Protocol-defined rules set the fee based on network demand and the computational resources the transaction consumes. Thus, the institution cannot choose the validator that processes its transaction, cannot negotiate the fee, and does not know the validator's identity before or after the transaction. Every other user on the network follows the same rules for their transactions.
As described, this bears some resemblance to the relationship between an email sender and the owner of a router that carries the message, or between a caller and the owner of a switch that completes the call. An internet protocol packet from a U.S. financial institution passing through infrastructure in a sanctioned jurisdiction is not thereby considered a sanctions violation: the same analytical approach applies to the neutral, protocol-mediated transmission at the consensus layer of a permissionless network. This distinction is codified in the BSA's own regulatory definition, which explicitly excludes those who "solely provide delivery, communication, or network access services used by a money transmitter to support money transmission services." The BSA distinguishes neutral carriage from transmittal, and sanctions analysis turns on this same characteristic of the relationship — the absence of choice, direction, or transaction.
Although an institution transacting on a permissionless network does have some contact with unscreened operators, this contact differs from what sanctions law regulates: in the latter case, neither party has chosen the other. To put it another way, in the nearly five years since OFAC issued its "Sanctions Compliance Guidance for the Virtual Currency Industry," there has been no enforcement action based on a validator proposing a block that happened to include a transaction from a sanctioned party, nor one based on market participants paying protocol-level fees.
Privacy and Compliance Are Compatible
A second institutional concern is privacy: can banks transact on a public ledger without exposing their client positions, counterparties, and strategies to competitors?
Early arguments for permissionless ledgers positioned full transparency as a compliance guarantee. Financial integrity requires something narrower: the ability for necessary information to be verified by the institution, its counterparties, and its regulators or supervisors. Cryptography has advanced sufficiently that institutions can prove compliance-relevant propositions — for example, proving a counterparty is not on the SDN List, or proving reserves exceed liabilities — without publicly exposing the data, such as the books and the identities of counterparties. Origin proofs allow a party to prove an asset did not originate from an identified illicit pool without exposing its transaction graph. Confidential transfer designs encrypt amounts and balances on the ledger while preserving a view key the institution can provide to examiners.
Taken together, these cryptographic advances provide regulators with greater assurance of security than a closed system. And they offer competitors absolutely no insight, making privacy no longer a reason to avoid building on permissionless networks.
Some of these technologies are already in production; others remain in development. Address rotation and account abstraction are in production, as are omnibus and layered custody structures that can remove client-level detail from the ledger; and messaging protocols for transmitting travel rule data alongside on-chain transfers. While confidential transfer with audit keys is live, its use at an institutional level remains limited today. Unauthorized state proofs and provenance proofs for designated data sets are still in pilot testing and research. However, solutions do exist: for example, Privacy Cash, a privacy protocol based on Ethereum and Solana, uses zero-knowledge proofs to enable confidential transfers and swaps.
A Risk Management Framework for Permissionless Networks
We propose nine components of a financial integrity program adapted to activity on permissionless networks: transaction-level controls that apply to the institution's customers and counterparties, largely in the same form as today; and network-level controls for the infrastructure itself.
These controls do not require identifying validators, entering into service level agreements with the protocol, or applying for membership to a gatekeeper, as some other features of permissioned networks do: current financial integrity law does not require these.
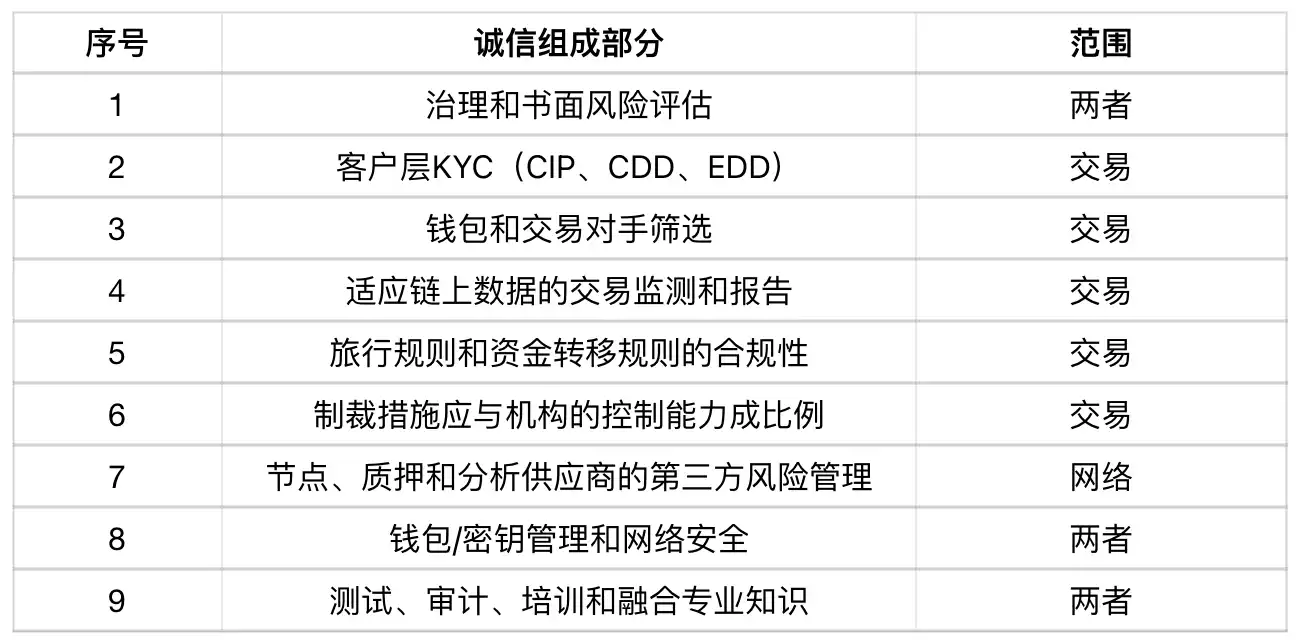
The proposed framework is also consistent with recent U.S. legislation, the GENIUS Act. GENIUS similarly adopts a framework where AML/CFT and sanctions controls reside at the application layer, operated by entities that know their customers and control the assets. The GENIUS Act requires entities approved to issue payment stablecoins to certify the existence of AML and sanctions compliance programs and maintain the technical capacity to execute lawful orders to freeze or destroy circulating stablecoins. These obligations are imposed on the issuer, not the permissionless network on which the stablecoin circulates.
Conclusion
A generation ago, regulated financial institutions faced an open, global, permissionless network that anyone could join, carrying traffic from legitimate and illicit users. These institutions moved their business onto the open protocols of the internet and built controls at the application layer. The same can be done today for permissionless networks.
Avoiding permissionless networks is not a financial integrity strategy; it is, in effect, abdicating the important role U.S. financial institutions play in building a robust, data-rich, risk-based dollar financial system. Dollar-denominated activity on permissionless networks is happening and will continue, whether U.S. financial institutions participate or not. The efficacy of U.S. financial enforcement depends on monitoring money flows, and the architecture of financial integrity laws — including their enforcement and supervision — relies on U.S. financial institutions observing the activities they are required to monitor. Forgoing the innovation and benefits of engaging with permissionless networks based on a misunderstanding of the relevant law or concerns about past regulatory stances unnecessarily limits traditional financial institutions' options for meeting client needs.






