The EU is telling cryptocurrency hardware and software wallet providers that they have 24 hours from awareness to report actively exploited bugs or severe security vulnerabilities affecting their products.
The measure is part of the EU’s Cyber Resilience Act (CRA), which took effect on Friday, according to an announcement from the European Commission.
Manufacturers must submit an early warning for severe vulnerabilities within 24 hours, followed by a full notification within 72 hours. A final report will be required 14 days after corrective or mitigating measures are available and within one month for severe incidents.
The EC said the new reporting requirements aim to better protect consumers and businesses from cyber threats. The measure extends to all products “with digital elements made available in the EU” and builds on the EU’s broader cybersecurity strategy.
Cointelegraph has approached the European Commission for more details surrounding the cybersecurity measures.
Related: German finance ministry proposes 25% crypto tax starting 2028: Report
Fines could reach $17 million
Companies that fail to adhere to the cybersecurity measures under Articles 13 and 14 may face an administrative fine of up to 15 million euros ($17.3 million) or 2.5% of worldwide annual turnover, depending on which figure is higher, according to the penalties section of the final draft.
Supplying incorrect, incomplete or misleading information will also subject companies to an administrative fine of up to 5 million euros.
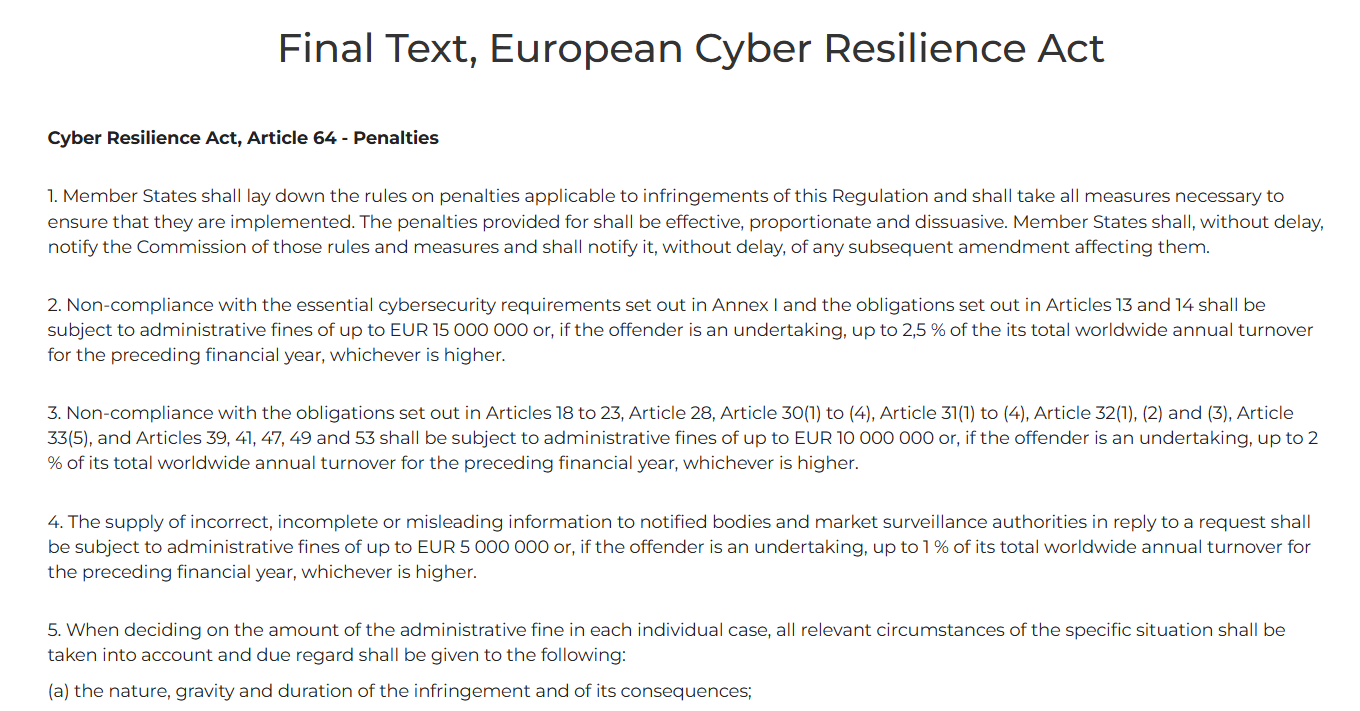
Excerpt from Final Text, European Cyber Resilience Act. Source: European-Cyber-Resilience-Act.com
The measure was revealed weeks after two popular hardware wallet providers disclosed user data breaches that could lead to phishing or social engineering attempts.
On Sept. 4, hardware wallet provider Trezor revealed that an additional 67,000 US customers were at risk from the data breach suffered by its shipping provider, ShipMonk, exceeding the initially estimated 14,000 users.
On Wednesday, Trezor and BitBox warned users about phishing emails disguised as urgent security notices after suspected compromises involving third-party email services.
In June, Layer-1 blockchain network Zilliqa warned that a vulnerability in the Zilliqa Ledger app could allow attackers to recover users’ private keys using publicly available onchain data.
Cointelegraph has approached wallet makers Trezor and Ledger for comment on how wallet providers would comply with the new reporting requirements.
Magazine: How Hong Kong is turning tokenized bonds into real market infrastructure