Author | Asher(@Asher_ 0210)
On September 6th, an attacker exploited a vulnerability in the Elements software to generate approximately 4,000 LBTC out of thin air and, through SideSwap's normal withdrawal channel, exchanged about 3,998.5 BTC from Liquid's multi-signature wallet, worth approximately $320 million.
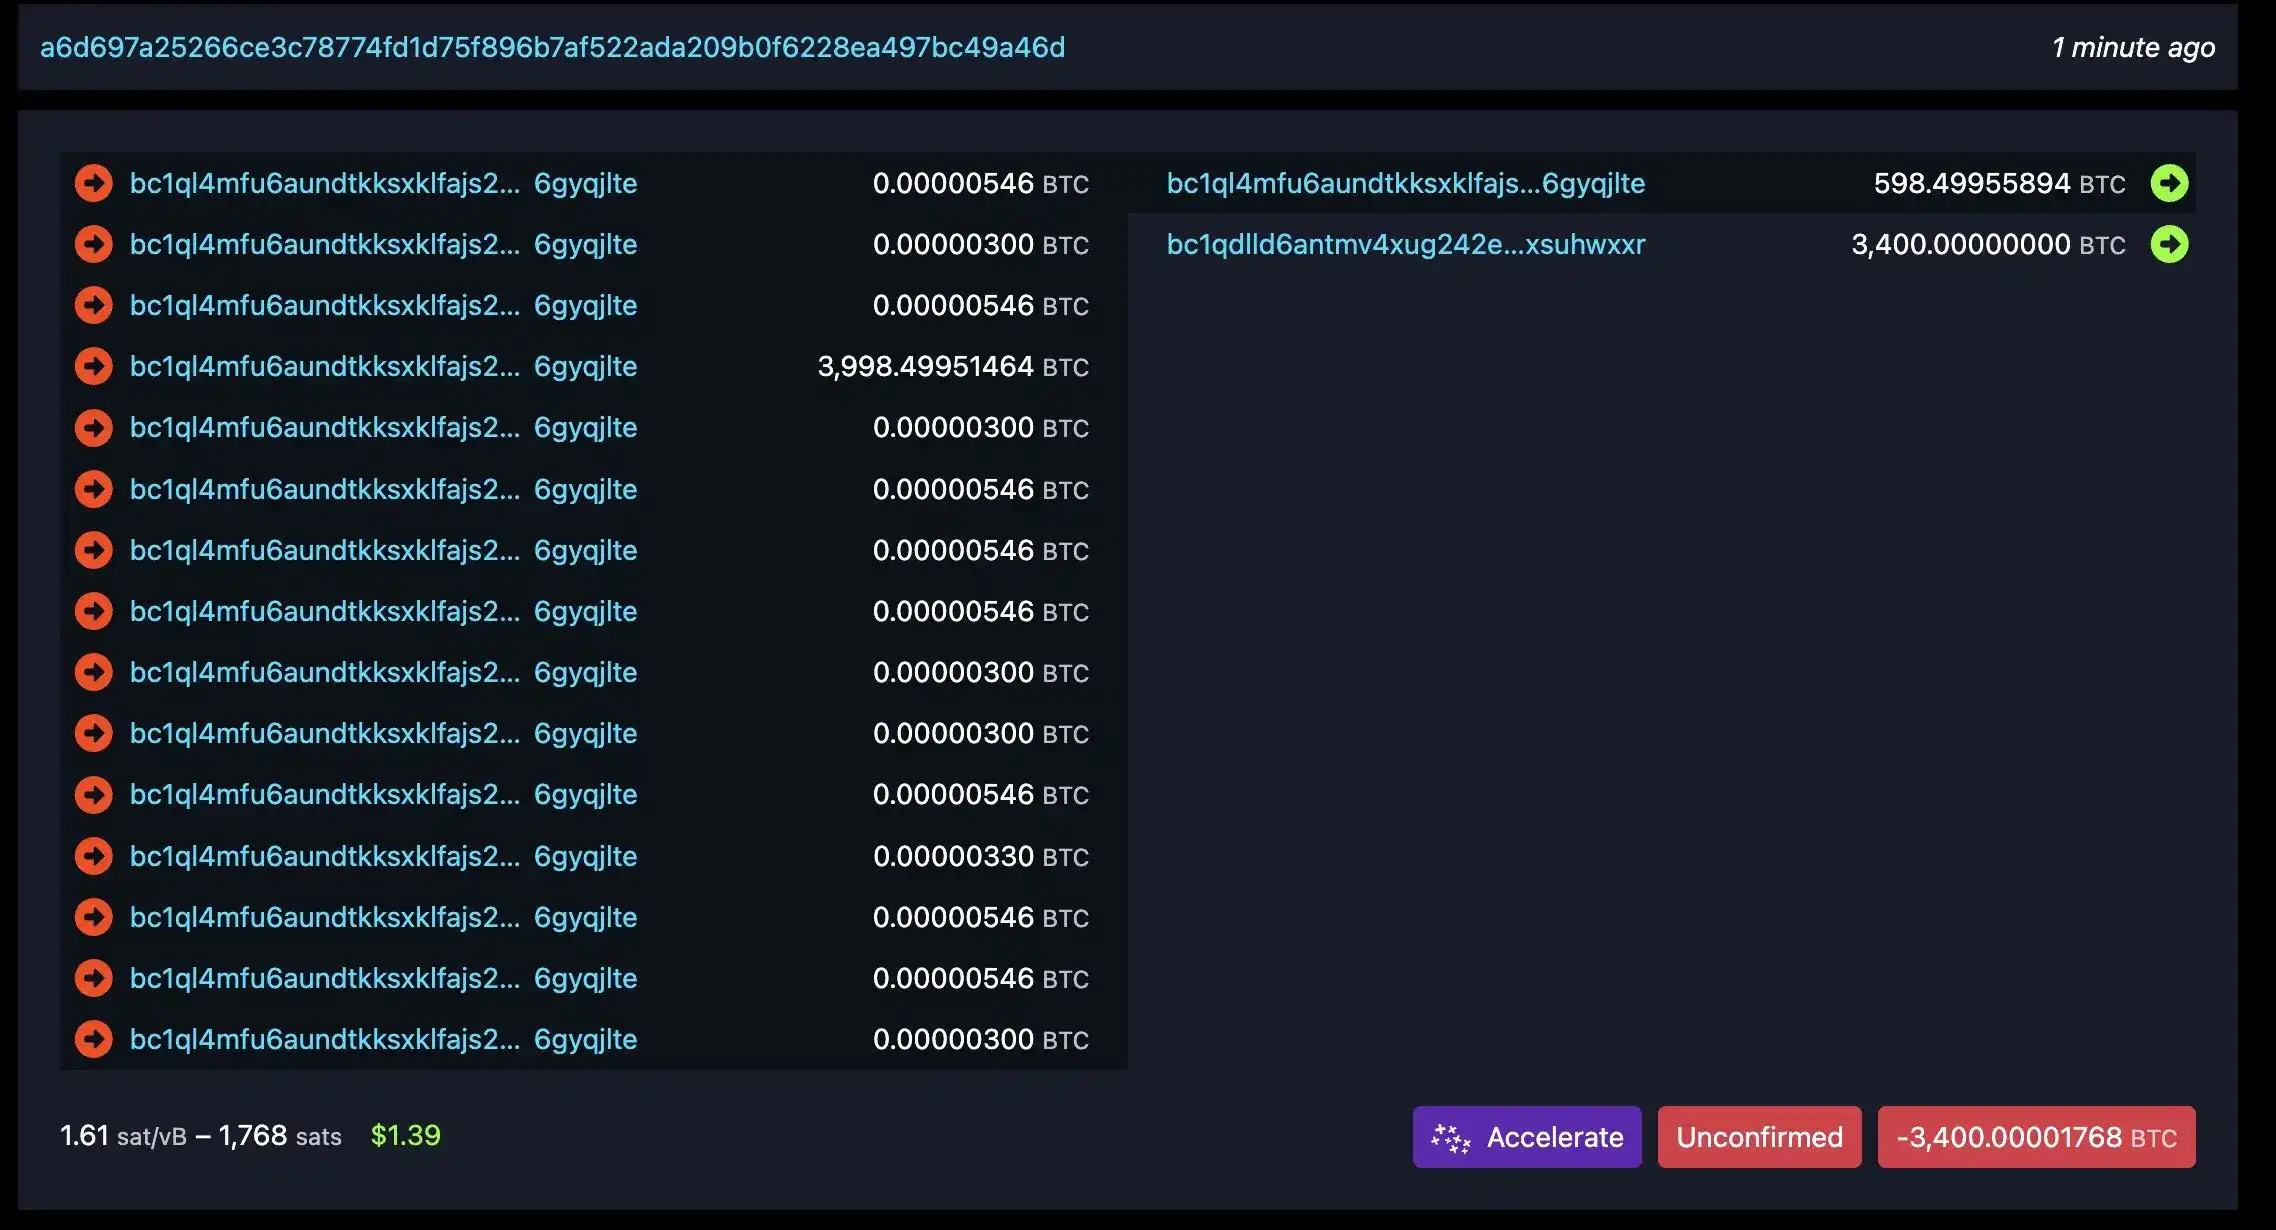
However, the attacker later left a message in a Bitcoin transaction: "We are white hats, please contact us on-chain." After Blockstream fixed the vulnerability, the attacker returned 3,400 BTC but kept the remaining approximately 598.5 BTC in an address under their control, worth about $47 million.
Currently, Blockstream is communicating with the attacker in an attempt to recover the remaining 598.5 BTC. The official statement also does not confirm it as a bug bounty.
Returning 85% and keeping 15%—is this a costly white hat operation, or did the attacker essentially set their own massive reward by using the return of funds as leverage?
Generating LBTC Out of Thin Air, Swapping for Nearly 4,000 Real BTC
Liquid Network is a Bitcoin sidechain launched by Blockstream in 2018. Unlike the Lightning Network, which primarily serves everyday payments, Liquid focuses more on Bitcoin settlement between exchanges and institutions, while also supporting the issuance of digital assets like stablecoins and securities. The number of institutions participating in Liquid's governance and operations has grown from the initial 23 to 87, and the total value of Real World Assets (RWA) issued on Liquid now exceeds $5 billion.
On September 6th, Liquid experienced its most severe security incident since its launch. The related withdrawals were completed in two stages. The attacker first withdrew about 2.5 BTC as a test, then transferred approximately 3,996 BTC. These two transactions accounted for about 95% of the Bitcoin reserves in the multi-signature wallet before the incident. After the funds were moved out, the wallet was left with only about 197 BTC. Liquid subsequently shut down its bridge nodes, paused network operations, and multiple exchanges suspended LBTC deposits and withdrawals.
This incident was not due to a leak of the multi-signature wallet's private keys; the Peg-out Authorization Key used by SideSwap to authorize withdrawals was also not stolen. The real issue lay in the underlying Elements software used by Liquid.
According to information disclosed by SideSwap, the attacker exploited a vulnerability in the Elements software to generate approximately 4,000 LBTC without real BTC reserve backing. These LBTC were then sent to SideSwap's Peg-out service. From the system's perspective, these LBTC generated via the vulnerability were indistinguishable from legitimate assets. Consequently, SideSwap followed the normal procedure of burning the LBTC and submitting a withdrawal request, prompting the Liquid multi-signature wallet to pay the corresponding real BTC to the attacker's address.
In simple terms, the attacker did not directly breach the wallet holding the BTC. Instead, they created a batch of "fake LBTC" that could deceive the system and then exchanged them for real BTC through the normal withdrawal channel.
The Liquid multi-signature wallet uses an 11-of-15 mechanism, meaning a withdrawal requires approval from at least 11 of the 15 multi-signature members. However, this incident demonstrates that multi-signature can only confirm that a withdrawal has received sufficient authorization; it cannot verify whether the LBTC entering the withdrawal process were generated by exploiting a vulnerability. When the asset verification step fails, even multiple subsequent signatures might approve an illegitimate transaction.
A Negotiation on the Bitcoin Blockchain
After transferring the funds, the attacker left a message in the OP_RETURN field of a Bitcoin transaction: "we are whitehats. contact us on chain."
Blockstream sent 1000 satoshis to the attacker's address, requesting they contact the security team. The two parties then engaged in on-chain communication via OP_RETURN, PGP signatures, and encrypted messages. The attacker stated they were willing to return "most of the funds" after the vulnerability was fixed and demanded that Blockstream ensure all bridge nodes were updated. Once the fix was complete, Blockstream informed the attacker via a signed message: "The bridge nodes are now patched. It is safe to return the funds."
On September 7th, the attacker sent 3,400 BTC back to the Liquid multi-signature wallet while transferring the remaining approximately 598.5 BTC to an address under their control. However, the publicly available on-chain information between the parties contains no agreement on how much BTC the attacker could keep, nor is the 598.5 BTC negotiated as a bug bounty.
Liquid's latest security incident report indicates that Blockstream is still communicating with the attacker, trying to recover the remaining 598.5 BTC. From this, it appears that Blockstream's prior agreement for the attacker to return "most of the funds" does not mean it approved the other party keeping BTC worth approximately $47 million. At least in the current official stance, these funds are still assets to be recovered, not a confirmed white hat bounty payment.
$47 Million: Bounty or Extortion?
Supporters of the attacker argue that if malicious hackers had discovered the vulnerability first, Liquid might have lost its entire Bitcoin reserve. In this case, the attacker demanded Blockstream fix the vulnerability first and ultimately returned 85% of the funds. Even if the nearly 600 BTC are not returned, Liquid still avoided a worse outcome compared to a total loss of funds.
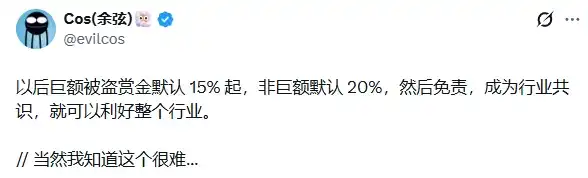
Cøbra, the anonymous owner of Bitcoin.org, believes white hats deserve rewards commensurate with the losses they helped prevent; Yu Xian, founder of SlowMist, also suggested that future large-scale theft incidents could gradually form a consensus of "starting from 15%" as a return bounty. In their view, higher bounties incentivize vulnerability discoverers to choose returning the funds rather than keeping them all.
The root of the controversy lies in the "procedure." Traditional white hat disclosure typically involves first reporting the vulnerability, then the project pays a reward based on established rules or negotiation results. The Liquid attacker, however, first withdrew almost the entire reserve and then unilaterally kept 15%. Charles Guillemet, CTO of Ledger, therefore questioned that this approach is closer to demanding payment under the condition of returning funds, rather than normal white hat behavior.
For Liquid, recovering 3,400 BTC only temporarily alleviates the reserve crisis. The fix for the vulnerability has entered internal and external review stages. The official plan is to urgently release Elements v23.3.4, followed by Functionary operators adjusting the network to reject the previously invalid Peg-out transactions and resume network operations.
Whether the remaining funds can be recovered and when Liquid will fully resume operations still depend on subsequent developments. However, the latest official statement has made the controversy clearer: the attacker can call themselves white hats, but they cannot unilaterally define the withheld $47 million as a bug bounty.