Written by: Liam 'Akiba' Wright
Compiled by: Saoirse, Foresight News
Circle has issued a warning: The resources required for quantum circuits designed to crack mainstream blockchain signature algorithms are continuously decreasing, citing a new low-resource record of 813 logical qubits.
Implementing USDC quantum migration directly exposes cross-ecosystem dependency issues: Every host blockchain, wallet, custodian, cross-chain bridge, and user account ultimately needs to adopt a more secure transaction authorization method.
Circle's current contract documentation records USDC deployment information for 37 mainnets. The company can protect its managed infrastructure and exercise token contract permissions on supported networks, but it cannot rotate user private keys, rewrite the signature systems of custodians, or unilaterally modify the signature rules of Ethereum, Solana, XRPL, and other public chains.
In a disclosure document on August 31, Circle called on developers to review their own cryptographic systems, audit third-party dependencies, and prepare for key rotation. As of September 2, USDC's market capitalization is approximately $73.6 billion, making this ecosystem coordination issue a matter of immense assets. If the migration only fortifies Circle's own keys but leaves old wallets, cross-chain bridges, or underlying blockchain paths exposed to risk, then the entire USDC ecosystem cannot be considered secure.
813 Qubits is a Reference Metric, Not a Countdown
Circle states that the 813 logical qubits are the low-resource consumption record updated on the ECDSA.fail website in August 2026. This data proves the improving resource efficiency of quantum circuit designs, but this number is easily misinterpreted by the public.
This open challenge specification targets the secp256k1 elliptic curve used by Bitcoin and Ethereum, optimizing reversible point addition circuits; the scoring method is the peak logical qubit width multiplied by the average number of Toffoli gates. Developers can reduce bit width by increasing the number of logic gates, or reduce logic gate consumption by increasing bit width. Therefore, the number 813 alone cannot fully describe a Shor's algorithm attack, circuit depth, error correction overhead, nor reflect the actual runtime of such an attack on physical hardware.
(Note: Toffoli gates are a key computational instruction in quantum computers. Quantum programs for cracking encryption algorithms heavily use this instruction. When evaluating quantum cracking capabilities, one must consider both the number of qubits and the quantity of such instructions.)
A paper from March 2026 clearly illustrates this trade-off. Researchers estimated that for an attack on a 256-bit elliptic curve discrete logarithm, one scheme requires fewer than 1,200 logical qubits and no more than 90 million Toffoli gates; another scheme requires no more than 1,450 logical qubits and 70 million Toffoli gates. The premise for this minute-level attack scenario is: a high-speed clock superconducting architecture, a physical error rate of 10^−3, a planar connection architecture, and fewer than 500,000 physical qubits.
Compared to the simple bit-width metric, these estimates represent a more complete resource model, but it still cannot determine when such hardware might become available.
Circle's external hardware comparison statement is also slightly inaccurate. Its article claims Google achieved 105 logical qubits with Willow. However, Google positions Willow as a 105-qubit processor; the corresponding *Nature* paper records an experiment using 105 physical qubits to complete a distance-7 surface code logical memory experiment, actually using 101 qubits. This is not the same concept as 105 logical qubits usable for an attack.
Advancing migration does not require setting an artificial deadline. The US National Institute of Standards and Technology (NIST) has already incorporated SLH-DSSA into the FIPS 205 standard and requires all organizations to begin replacing quantum-vulnerable cryptographic schemes immediately. The 2035 timeline proposed by NIST merely represents when these algorithms will be deprecated and removed from the standard, not a prediction of a "Quantum Attack Day."
The true criterion for initiating migration is ecosystem readiness: Public chains need sufficient time to add new signature verification rules; wallets and custodians need proven key rotation processes; users need a transition period allowing traditional cryptographic authorization and post-quantum authorization to run in parallel, avoiding liquidity fragmentation or user assets being locked.
Arc is Just One Layer Within the 37-Chain System That Circle Controls
Arc allows Circle to more directly build post-quantum cryptographic support capabilities, but the official documentation splits the logic into multiple layers, while Circle's external disclosures simplify it as "supporting SLH-DSA."
Arc's execution layer documentation introduces a precompiled program capable of verifying SLH-DSA-SHA2-128s signatures. This precompiled component allows smart contracts to verify corresponding signature types, but it does not automatically replace the signature mechanisms used for ordinary network transactions.
The Arc Custody Guide still uses standard secp256k1 ECDSA for transaction signing. Its post-quantum roadmap plans: launch an optional beta version of post-quantum wallet signatures at mainnet launch, with post-quantum validator signature functionality to follow. Circle also states that Arc has not finalized its post-quantum transaction signature scheme, and the migration phase will be compatible with a hybrid ECDSA signature mode.
Arc can serve as a testing ground for hybrid signature schemes. However, relying solely on Arc's upgrade cannot make USDC quantum-secure on Ethereum, Solana, and the remaining 35 mainnets.
USDC Quantum Migration Involves 37 Independent Network Paths
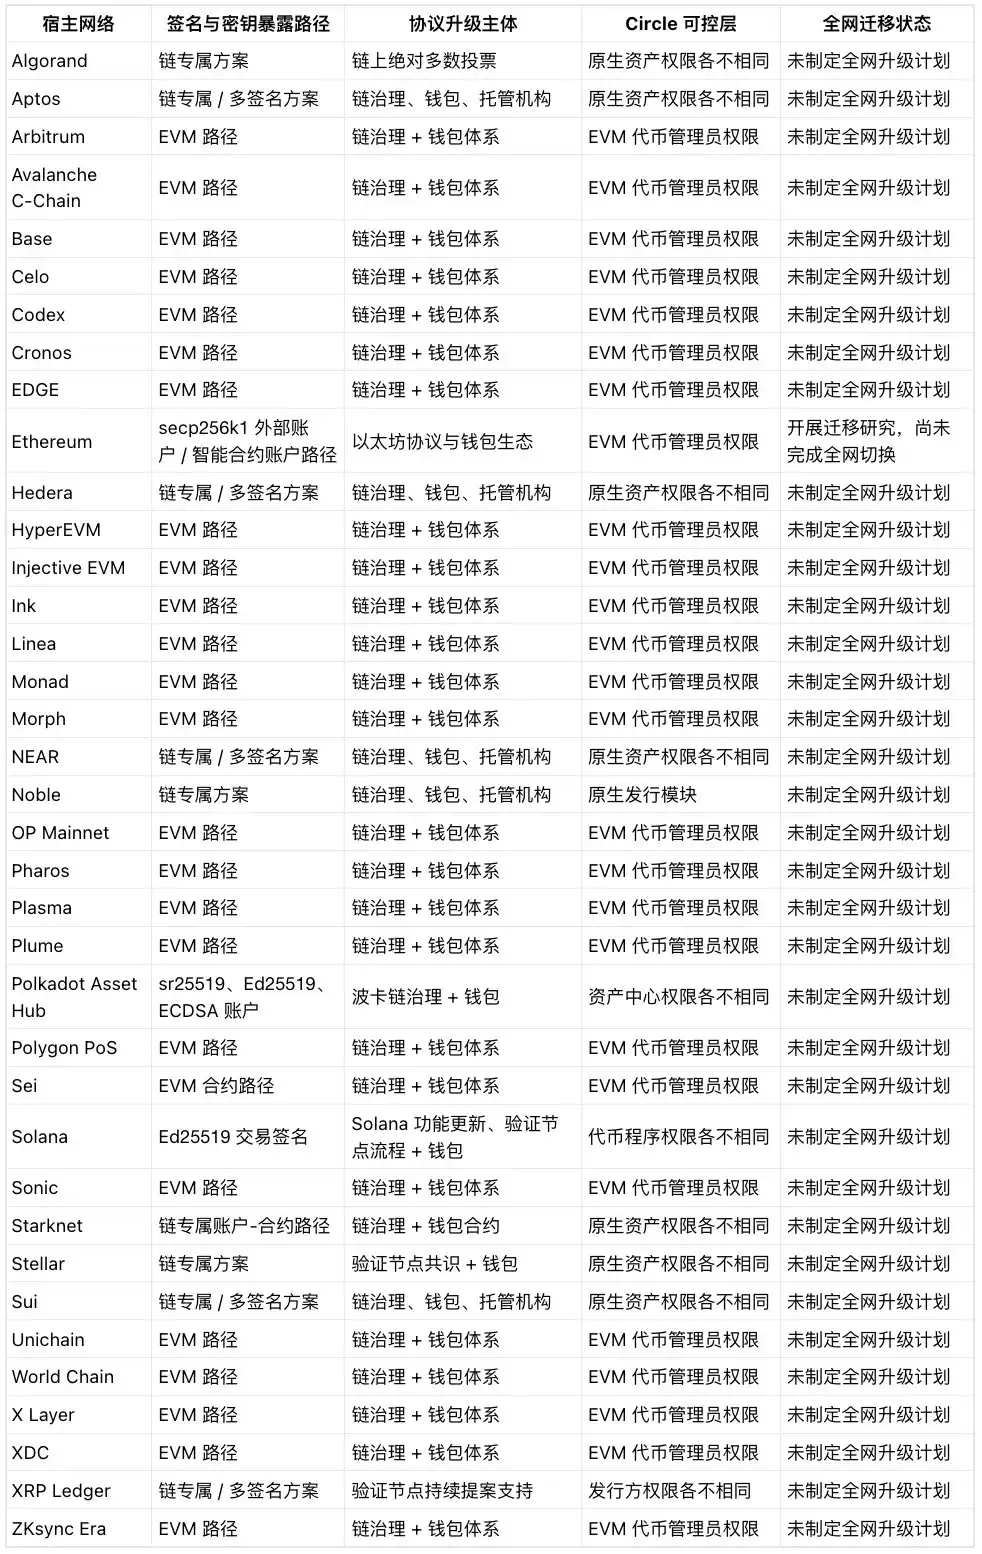
The number of networks Circle publicly announces itself is fluid. The text on its USDC page as of June 29, 2026, notes 35 networks, but actually lists 37 names. The contract address summary table referenced in this article records 37 mainnets. Counting the Arc testnet, the Circle Mint list reaches 38, therefore the testnet is excluded from the count.
The table below distinguishes between verifiable signature types and host chains requiring independent cryptographic audits. "EVM Path" represents Ethereum-style externally owned accounts (EOAs), which by default use secp256k1 ECDSA, allowing public key recovery after signing; smart contract accounts can use contract-defined custom verification logic. "Chain-specific Scheme" indicates that the official documentation of a public chain does not explicitly unify the signature algorithm, not mandating a specific scheme. The status column records whether the public chain has fully implemented a network-wide post-quantum upgrade; it does not indicate the absence of exploratory research and development work on the chain.
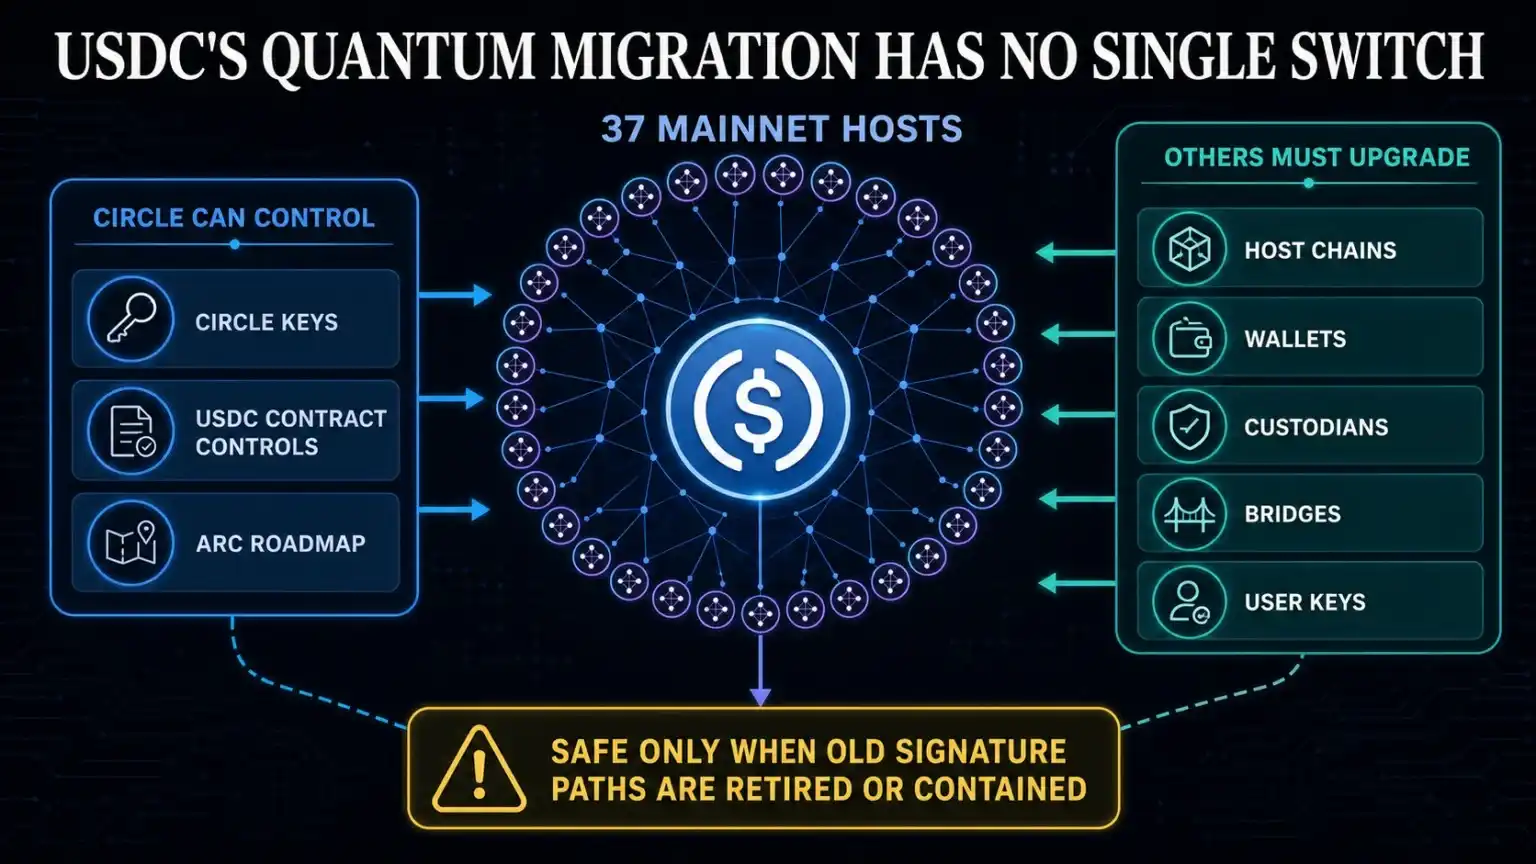
USDC's quantum security upgrade cannot rely solely on unilateral action by Circle. All 37 public chains, wallets, custodians, cross-chain bridges, and users must upgrade simultaneously, completely phasing out old signature mechanisms; only then can the whole be considered truly secure.
Examples illustrate the point: There is no single unified deadline that can cover the entire ecosystem. Solana transactions use Ed25519 signatures; Polkadot supports sr25519, Ed25519, and ECDSA accounts simultaneously. Even comparing within Ethereum, migration schemes for externally owned accounts and smart contract wallets are already different, let alone non-EVM public chains.
The upgrade decision mechanisms of each public chain are also completely different. XRPL amendment proposals require over 80% of trusted validators to support them for two consecutive weeks; Algorand protocol modifications require on-chain absolute majority voting; Stellar network upgrades rely on validator consensus. Circle has no authority to intervene in any of these decisions.
Freezing and Reissuing Permissions Cannot Complete User Key Rotation
Circle holds several key control capabilities at the token layer. Its EVM fiat token design incorporates permissions for minting, burning, pausing transfers, blacklisting, and contract upgrades. The USDC Terms of Service also state that, under specific circumstances, it has the power to freeze addresses and suspend services.
These capabilities can control risk when security incidents occur in contracts. Under permissible conditions, Circle can freeze addresses, stop minting or transfers, and execute redemptions or token reissuance according to legal and business rules. However, address freezing cannot fix the risk posed by stolen private keys, nor can it modify the underlying public chain's signature verification logic.
The responsible entities for key risks differ:
- Circle: Must rotate the issuer and contract management credentials under its control.
- User / Custodian: Must use wallets and public chains compatible with new signatures to move assets from at-risk accounts.
- Cross-chain Bridge Operators: Must protect their own signatures and contract permissions, while also coordinating liquidity across both sides.
- Underlying Chain Communities: Approve and implement protocol-layer changes.
- Wallet Providers, Hardware Wallets, Exchanges: Maintain compatibility with both old and new signature algorithms during the transition period.
Therefore, the weakest link may not be the public chain with the slowest technological iteration. Custodians unable to quickly rotate keys for thousands of accounts; emergency control logic for cross-chain bridges still relying on vulnerable keys; large numbers of users not migrating assets before the old signature scheme is phased out — any of these can become attack vectors.
A feasible implementation plan cannot just set a single block height as a switch. Each operator needs to inventory risk/security keys, validated target account types, software/hardware adapted for new signatures, and also formulate disposal strategies for unmigrated balances. Hybrid signature modes must have a clear endpoint, not allowing traditional signatures to be retained indefinitely as a bypass. Circle can set milestones for its own contracts and services, but each public chain ecosystem independently decides when and how to deactivate traditional signature paths.
Even Without a Definitive 'Quantum Attack Day,' the Urgency of Migration is Real
The value of Circle's disclosure is that it turns post-quantum cryptographic preparation into an operational plan that needs to be implemented now. The 813-qubit record proves that while hardware teams tackle error correction technology, attack quantum circuits will continue to be optimized. NIST's open standards also provide developers with testable implementation options.
However, this disclosure also has exaggerations: directly comparing the 813 logical qubits for attack to Willow's 105 physical qubits, placing them on the same scale. Simultaneously, the article underestimates the practical gap: the difficulty between verifying SLH-DSA signatures inside Arc and fully implementing USDC's authorization, settlement, and asset recovery across dozens of production public chains is worlds apart.
Circle can optimize systems under its jurisdiction. But only when host chains, wallets, custodians, cross-chain bridges, and all users complete their migration, and all traditional signature paths are either phased out or strictly restricted, can Circle claim that USDC as a whole has achieved quantum security. This is a large-scale migration project involving multiple veto powers, far from simply flipping a cryptographic switch.